KPMG Canada reports cyber incident involving unauthorized access to clients' tax documents
KPMG Canada says an unauthorized party accessed some clients' tax documents, and questions remain about how much data was affected and the risk of fraud.
Translated from Arabic. Read the original بالعربية
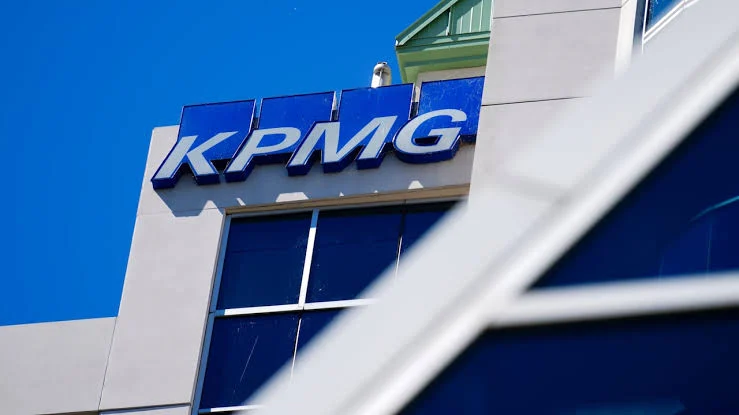
TORONTO — KPMG Canada, the accounting, audit and advisory firm, has acknowledged a cybersecurity incident that allowed an unauthorized party to access some of its clients' tax documents.
The company said it is in contact with those affected. It has not yet said how many clients are involved or how many files were accessed without authorization.
The incident was disclosed on Wednesday evening, amid growing attention to attacks targeting professional and financial institutions in Canada because of the sensitive information they hold on behalf of individuals and businesses.
What has the company said about the breach?
Company spokesperson Sonia Cloutier Bosworth said the firm has taken steps to secure its systems and contain the incident.
She said she is confident the affected information is not available online, and that ongoing monitoring has shown no indication it has been used illegally.
However, this reflects the company's current assessment. It does not mean the investigation has uncovered every detail of the incident or definitively ruled out any later risk.
The firm has not said when the unauthorized access began, how it happened, or whether the data was copied outside its systems.
Tax documents raise privacy concerns
The incident is particularly significant because tax documents can contain sensitive financial and personal information, depending on the type of file, such as income, addresses and data linked to tax returns.
However, the company has not published a list of the specific information found in the affected files, so it cannot be stated that identification numbers or bank account details were leaked.
Access to a document is different from its public release or its use in fraud. That distinction should be kept in mind when assessing the risk, especially while technical checks continue and affected clients are being notified.
Official warning about impersonation of tech support staff
The announcement follows a warning issued on October 28 by the Canadian Centre for Cyber Security about voice phishing campaigns targeting organizations in the country.
According to the warning, attackers pose as internal technical support teams and then direct employees to fake login pages to steal their credentials.
The Centre noted that organizations in the legal and financial sectors have been targeted in recent months. However, the information it published does not link this campaign specifically to the KPMG incident, so voice phishing cannot be considered a confirmed cause of the breach.
What does data protection law say?
Canada's federal private-sector privacy law, the Personal Information Protection and Electronic Documents Act (PIPEDA), requires organizations to report breaches that pose a real risk of significant harm, and to notify affected individuals when that threshold is met.
It also requires organizations to keep records of security breaches, even when not all of them have to be reported to the Privacy Commissioner of Canada. It is not clear from the available statement whether KPMG has filed a formal report with the Commissioner, or whether the incident met the legal reporting threshold.
Why are consulting firms a sensitive target?
Accounting and consulting firms handle data for a large number of clients in one place, and their work can include tax returns, financial reports and professional correspondence.
As a result, any unauthorized access may require a review of many files, even when the suspected activity is limited.
The incident highlights the importance of monitoring professional accounts and restricting access permissions, without assuming that every client of the firm has actually been affected.
What should clients do?
Clients who receive a notice from the firm should verify it through the company's official channels and avoid clicking unexpected links that claim to offer compensation or urgently ask for financial information to be updated.
They can ask the firm directly about the type of documents affected, the date of the incident and the recommended precautions. It is also advisable to watch for phishing messages and impersonation attempts, especially those that include tax information or unusual payment requests.
Basic questions remain open about the scope and method of the access. Until further findings are released, what is confirmed is that an unauthorized party accessed some client files, not that they were published online or misused.
More from Hala Canada
- Carney avoids position on Quebecor's $31-billion bid for Telus, stresses competition
- Quebec has Canada's longest emergency room stays, Montreal Economic Institute report finds
- 61% of Toronto-area residents rate emergency room wait times as bad, poll finds
- Six outcomes of Carney's trip to Asia and Ireland, from Trump meeting to deals with China and the Philippines
- 22 chickens escape from truck in Toronto parking lot as firefighters step in to round them up
- Toronto drug checking program finds new synthetic opioid in fentanyl samples